Introduction
Arceris Ai Security Gateway secures AI traffic.
What is Arceris Ai Security Gateway?
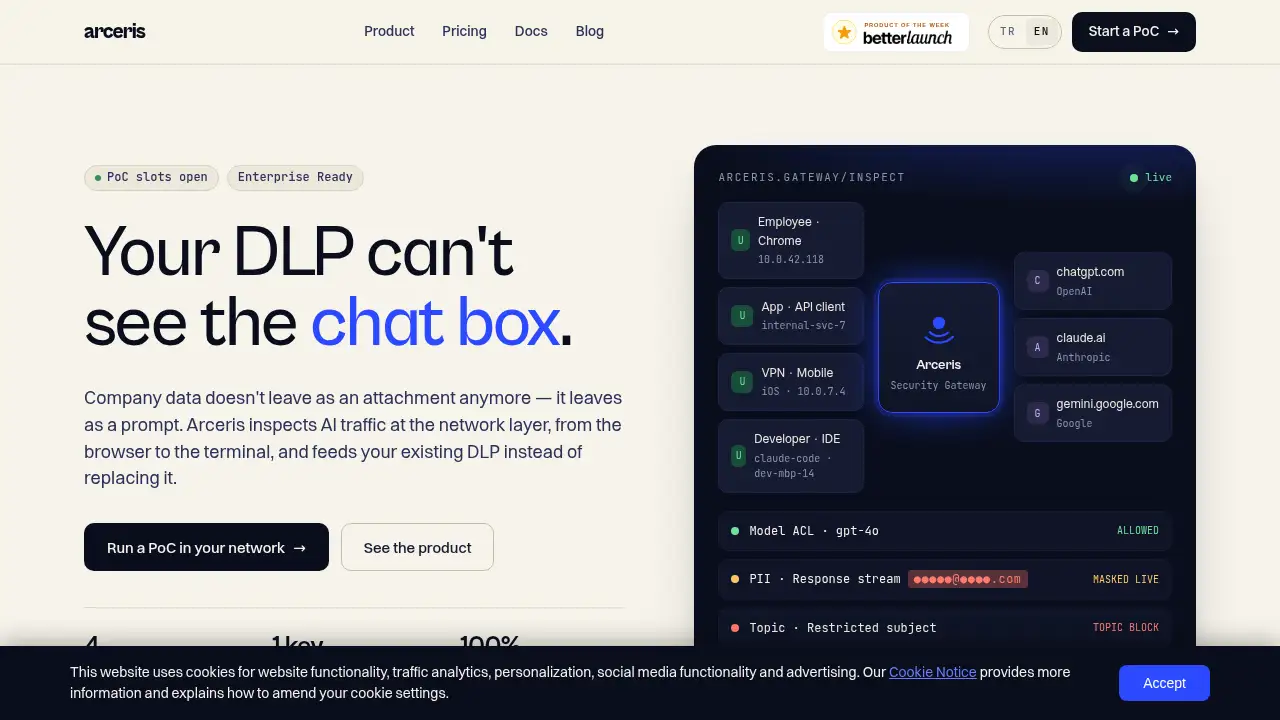
Arceris AI Security Gateway is a self-hosted AI security gateway for organizations that need control over corporate AI usage. This AI security gateway inspects AI traffic at the network layer, covering browser sessions, API clients, mobile devices, terminals, and IDEs. It addresses a common gap: many DLP tools and API-only AI gateways cannot see data typed into chat boxes or AI coding assistants. The AI security gateway feeds existing DLP systems rather than replacing them, and it can decrypt and re-encrypt HTTPS AI traffic for inspection. It suits security, compliance, IT, and platform teams that want AI data security without relying on a cloud-dependent service. Core capabilities include AI traffic inspection, PII redaction, prompt injection defense, model access control, and audit logging. As a self-hosted AI security gateway, it is positioned as transparent and sovereign because it runs in the organization’s own infrastructure and stores real provider keys encrypted locally.
Key Features of Arceris Ai Security Gateway
Network-Level AI Traffic Inspection
Inspect HTTPS AI traffic in real time across browser tabs, API clients, mobile devices, and developer tools. This AI security gateway enables network-level AI traffic inspection for AI usage that API-only tools may miss.
Unified AI API Gateway
Route every AI provider through one endpoint with one key per user. The AI security gateway stores real provider keys encrypted in the organization’s infrastructure and applies redaction, access control, rate limits, spend limits, and full logging to each call.
Developer and IDE Coverage
Enroll developer devices in about one minute so AI coding tools such as Claude Code, Gemini CLI, Cursor, and VS Code route through the gateway automatically. This AI security gateway extends AI coding tools security and policy enforcement to terminals and editors.
Live PII Redaction
Detect and mask 28+ data types, including national IDs, IBANs, cards, keys, and JWTs, as responses stream word by word. PII redaction happens in the stream before sensitive data reaches the screen, which is a key benefit of this AI security gateway.
Injection Defense and Topic Controls
Block current prompt injection and jailbreak phrasings in English and Turkish, and apply topic-aware policy to restricted subjects. Prompt injection defense can keep sensitive topics on approved models only through the AI security gateway.
Image and File Security with OCR
Inspect files uploaded to AI services in real time using built-in OCR. The AI security gateway detects and blocks sensitive data hidden inside screenshots, PDFs, and contracts before they reach the LLM.
Model ACL and Smart Routing
Define who can interact with which model and route sensitive prompts to local LLMs when data residency matters. Model access control in this AI security gateway supports policy by user, team, model, and topic.
Audit and SIEM Integration
Record every blocked, masked, or observed event with timestamp and attribution. The AI security gateway lets teams filter, group repeated detections, search millions of events, and send audit data to SIEM tools.
Use Cases for Arceris Ai Security Gateway
Preventing Sensitive Data Leakage in Chatbots
Security teams can inspect employee prompts in ChatGPT, Claude, Gemini, and similar services. Live PII redaction and blocking in this AI security gateway reduce the risk of customer emails, IDs, API keys, or contract details leaving the network.
Securing AI Coding Assistants
Development teams use AI coding tools in terminals and editors every day. Arceris AI Security Gateway applies the same AI data security policy to Claude Code, Gemini CLI, Cursor, and VS Code, helping prevent secrets such as .env files from being pasted into prompts.
Enforcing AI Acceptable Use Policy
Compliance teams can use topic controls, model ACL, and audit logs to enforce acceptable use. This AI security gateway can block restricted subjects or limit them to approved models while giving reviewers a clear event trail.
Shadow AI Discovery and Visibility
Organizations often have more AI usage than API dashboards show. Network-level AI traffic inspection from this AI security gateway provides visibility into browser, mobile, and developer AI interactions, supporting Shadow AI discovery and better policy decisions.
How to Use Arceris Ai Security Gateway
- Request a demo or proof-of-concept slot to review deployment requirements and confirm the AI security gateway fits the network and compliance needs.
- Deploy the self-hosted AI security gateway inside the organization’s infrastructure and roll out the enterprise CA as directed by the vendor’s installer.
- Connect AI providers through the unified AI API gateway, or enroll developer devices so IDE and CLI traffic routes through the AI security gateway.
- Configure policies for PII redaction, model access control, topic restrictions, prompt injection defense, rate limits, and spend limits.
- Review live events and audit logs, then integrate alerts or records with existing DLP and SIEM workflows.
Target Audience for Arceris Ai Security Gateway
- Security teams that need AI traffic inspection from an AI security gateway and AI data security controls.
- Compliance and legal teams managing employee AI use and data residency concerns.
- IT and platform teams deploying a self-hosted AI security gateway.
- Development teams using AI coding tools in terminals and editors.
- Organizations that want an AI security gateway to feed existing DLP systems instead of replacing them.
Is Arceris Ai Security Gateway Free?
Arceris AI Security Gateway does not list public pricing on the provided homepage content. The page mentions “PoC slots open” and “Enterprise Ready,” which suggests proof-of-concept access and enterprise sales engagement. A 30-minute demo is available to see live PII blocking and Shadow AI discovery. For exact pricing and plan details, contact the vendor or check the official website.
| Plan | Price | Features |
|---|---|---|
| Public pricing | Not listed | Enterprise-ready AI security gateway; PoC slots mentioned |
| Demo / PoC | Contact vendor | 30-minute demo; live PII blocking and Shadow AI discovery |
Arceris Ai Security Gateway's Pros and Cons
| Aspect | Pros | Cons |
|---|---|---|
| Deployment | 100% self-hosted and air-gap ready; one installer and enterprise CA rollout mentioned | Requires internal deployment and CA management |
| Visibility | Covers browser, API, mobile, and developer tools; network-level AI traffic inspection | Network inspection may need careful rollout and testing |
| Data protection | Live PII redaction, OCR for files, model access control, audit logging | Public pricing is not listed |
| Developer coverage | Supports IDE and CLI AI tools with fast enrollment | Coverage depends on supported tools and device enrollment |
| Operations | SIEM-ready audit logs and live event console | Policy setup needs input from security and compliance teams |
Frequently Asked Questions about Arceris Ai Security Gateway
What makes Arceris AI Security Gateway different from API-only gateways?
Arceris AI Security Gateway inspects AI traffic at the network layer, so it can cover browser chats, mobile devices, terminals, and IDEs. API-only tools may see API calls but miss data typed into chat boxes. This AI security gateway is built for that broader visibility.
Does Arceris replace an existing DLP system?
No. The AI security gateway is designed to feed existing DLP systems rather than replace them. It adds AI traffic inspection and PII redaction for AI interactions that traditional DLP may not see.
Which AI services and developer tools does it support?
The homepage lists ChatGPT, Claude, Gemini, Claude Code, Gemini CLI, Cursor, and VS Code. The AI security gateway also describes a unified AI API gateway for multiple AI providers.
How does PII redaction work?
Arceris uses 28+ built-in detectors for national IDs, IBANs, cards, keys, and JWTs. This AI security gateway masks sensitive data live in the response stream before the data reaches the user’s screen.
Is Arceris AI Security Gateway self-hosted?
Yes. It is described as self-hosted, transparent, and sovereign, with real provider keys stored encrypted in the organization’s own infrastructure. The comparison table also mentions air-gap readiness for this AI security gateway.
Where can I find pricing?
Public pricing is not listed in the provided content. The vendor mentions PoC slots, enterprise readiness, and a 30-minute demo, so teams evaluating an AI security gateway should contact the vendor for pricing and deployment details.
Arceris Ai Security Gateway Tags
Arceris AI Security Gateway, AI security gateway, AI traffic inspection, PII redaction, self-hosted AI security, AI data security, AI DLP, prompt injection defense, model access control, AI coding tools security, Shadow AI discovery, enterprise AI security