Introduction
HodeiShield platform: security, risk, and compliance
What is HodeiShield?
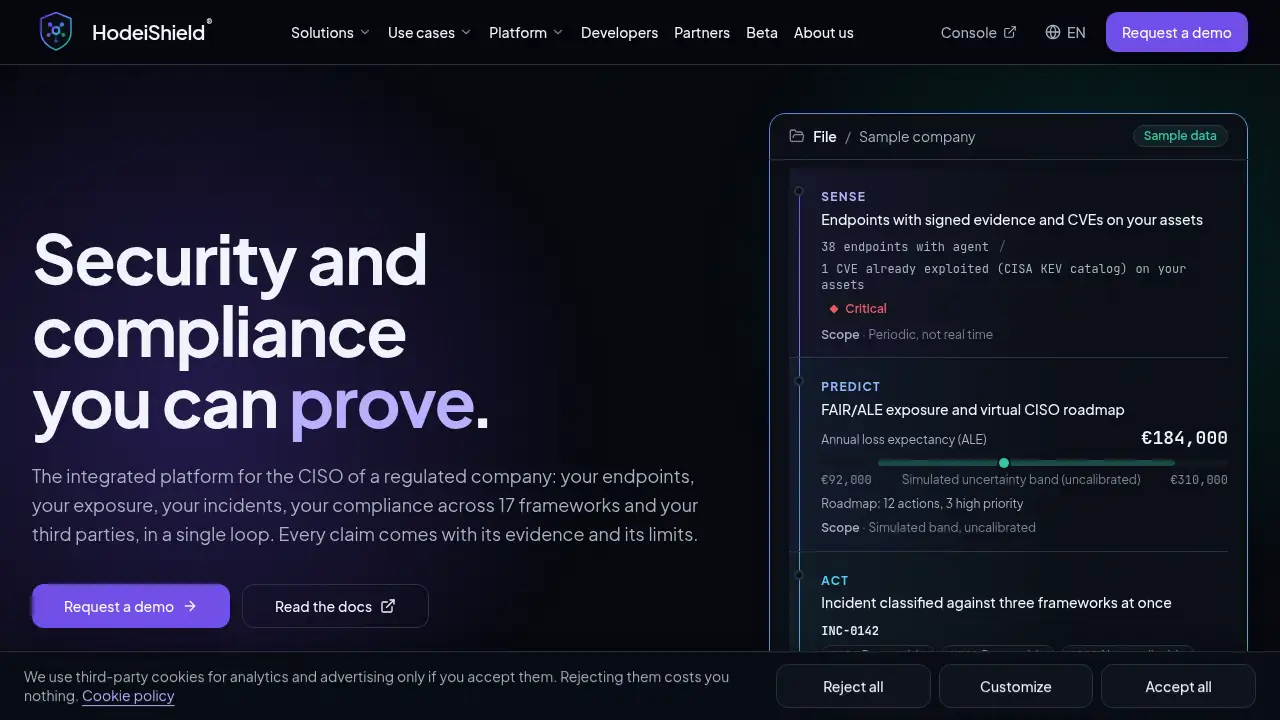
HodeiShield is an integrated security and compliance platform built for CISOs and security leads at regulated companies. It brings endpoint evidence, exposure management, incident handling, third-party risk, compliance tracking, and signed attestations into one traceable cycle. HodeiShield is a product of Hodeitek SL.
The problem it addresses is common in regulated environments: security, compliance, and vendor data often live in spreadsheets and separate tools that drift out of date between audits. Frameworks such as NIS2, DORA, and Spain’s ENS expect current evidence across the organisation and its supply chain. HodeiShield platform connects evidence collection, risk quantification, human-approved actions, and third-party proof so that audit readiness is based on current, owned, and expiring evidence rather than old snapshots.
HodeiShield is suitable for security leaders who need a clearer view of technical posture and compliance maturity without losing traceability. It is especially relevant for teams preparing for multi-framework compliance, third-party risk management, exposure management, and board-level risk reporting.
Key Features of HodeiShield
Signed Endpoint Evidence
HodeiShield uses an agent for Windows, macOS, and Linux that runs 172 checks and sends digitally signed observations. The console rejects any evidence that fails verification, which helps keep endpoint security data trustworthy.
Exposure Radar with KEV Priority
The platform lists CVEs on your assets and puts actively exploited vulnerabilities first. This supports exposure management by helping teams focus on known exploited issues before lower-priority findings.
FAIR/ALE Risk Quantification
HodeiShield quantifies and simulates FAIR/ALE exposure in euros per vendor and across the portfolio. It provides a reproducible point estimate with a simulated uncertainty band, giving security leaders a financial view of risk for board discussions.
Multi-Framework Compliance
HodeiShield maps evidence to the canonical controls of 17 compliance frameworks, including NIS2, ENS, DORA, GDPR, EU AI Act, ISO/IEC 27001, SOC 2, and NIST CSF 2.0. Evidence has an owner, a validity date, and a status, and it is reused across frameworks through a crosswalk.
HodeiAI with Human Approval
HodeiAI proposes actions, but a person with a write role must approve every execution. Approval is single-use, valid for 15 minutes, and bound to the hash of the exact proposal, which keeps automation under human control.
Signed Attestations and Trust Center
Every published Trust Center issues attestations signed with ML-DSA-65 (FIPS 204), with the signature kept separate from the attested document. Third parties can verify an attestation offline using an open-source verifier and the public key.
Third-Party Risk Management
HodeiShield supports vendor scans, questionnaires, and dependency checks, and matches vendor SBOMs against CVEs. This helps teams manage supply chain risk and third-party risk management in the same cycle as internal evidence.
Incident Management
The platform classifies incidents against DORA, NIS2, and GDPR, tracks deadlines, and prepares drafts. This supports incident management and regulatory reporting workflows without treating every incident the same way.
Use Cases for HodeiShield
Preparing for NIS2, DORA, and ENS Audits
HodeiShield helps teams collect current evidence, assign owners, and track expiry dates across NIS2, DORA, and ENS controls. The platform expresses coverage over canonical controls rather than making a blanket pass claim.
Managing Third-Party and Supply Chain Risk
Security teams can combine vendor questionnaires, external scans, SBOM data, and CVE matching in one third-party risk management workflow. This gives a clearer view of supplier exposure and dependencies.
Board Reporting and Risk Quantification
HodeiShield provides a board dashboard and report templates, alongside FAIR/ALE exposure in euros. This helps translate technical risk into financial terms without hiding uncertainty.
Incident Classification and Response
Teams can log incidents and classify them against DORA, NIS2, and GDPR requirements. Deadlines and draft outputs support a more structured incident management process.
Verifying Attestations Offline
Third parties can check a signed attestation with a public verifier, the public key, and standard tools. The process confirms integrity, origin, and time, but it does not replace an audit or prove that the attested content is true.
How to Use HodeiShield
- Request a demo or apply to the beta program through the official HodeiShield website.
- Connect endpoints and suppliers so the platform can collect signed evidence from agents, scans, questionnaires, and SBOM data.
- Map evidence to the relevant compliance frameworks and assign owners, validity dates, and statuses.
- Review FAIR/ALE risk exposure in euros and use HodeiAI proposals only through human approval.
- Publish a signed attestation in the Trust Center and share it with third parties who can verify it offline.
Target Audience for HodeiShield
- CISOs and security leads at regulated companies
- Compliance, audit, and governance teams managing multiple frameworks
- MSSPs and partners testing or delivering managed security services
- Organisations preparing for NIS2, DORA, ENS, ISO/IEC 27001, or SOC 2
- Boards and risk teams that need euro-based exposure reporting
- Companies managing third-party risk and supply chain security
Is HodeiShield Free?
HodeiShield is in beta from 2 November, with three months at no cost. Access is limited, applications are open until 31 December 2026, and the beta has no SLA. No standard public pricing plan is listed in the reference information.
| Plan | Price | Features |
|---|---|---|
| Beta | No cost for three months | Limited places, no SLA, access to the HodeiShield platform for testing and feedback |
For current availability and pricing details, check the official HodeiShield beta page or contact the vendor through the product website.
HodeiShield's Pros and Cons
| Aspect | Pros | Cons |
|---|---|---|
| Platform scope | Combines endpoint evidence, exposure, incidents, compliance, third-party risk, and attestations in one cycle | Broad scope may require time to configure and adopt |
| Compliance | Covers 17 frameworks, including NIS2, ENS, DORA, ISO/IEC 27001, and SOC 2 | Coverage depends on the organisation’s own evidence and does not guarantee audit pass |
| Risk reporting | Provides FAIR/ALE exposure in euros with an uncertainty band | Risk estimates are uncalibrated and should be reviewed with context |
| Attestations | Signed attestations can be verified offline with an open-source verifier | Attestations prove integrity, origin, and time, not the truth of the content |
| Automation | HodeiAI actions require explicit human approval | Today the only executable action is creating a risk register entry |
| Data location | Application, database, and storage are managed in the EU by OVH in Gravelines, France | Cloudflare acts as DNS, CDN, and TLS in the request path |
| Beta status | Three months at no cost during beta | Limited places, no SLA, and product still evolving |
Frequently Asked Questions about HodeiShield
What is HodeiShield?
HodeiShield is an integrated platform for CISOs that connects endpoint security, exposure management, incident management, third-party risk, 17 compliance frameworks, and signed attestations. It is designed for regulated companies that need traceable evidence and current compliance posture.
Which compliance frameworks does HodeiShield cover?
HodeiShield covers 17 frameworks, including NIS2, ENS, DORA, GDPR, EU AI Act, ISO/IEC 27001, ISO/IEC 42001, SOC 2, NIST CSF 2.0, PCI DSS v4.0, HIPAA, CMMC 2.0, Cyber Essentials, UAE IA (NESA), SAMA CSF, Saudi ECC-1:2018, and Nigeria NDPA 2023.
Does HodeiShield act on its own?
No. HodeiAI proposes actions, but a person with a write role must approve every execution. Approval is single-use, valid for 15 minutes, and bound to the hash of the proposal. Autonomous execution is blocked and the kill switch fails closed.
Can HodeiShield attestations be verified offline?
Yes. HodeiShield attestations use ML-DSA-65 signatures, and third parties can verify them offline with an open-source verifier, the public key, and tools such as bash, OpenSSL, Python, Docker, or Podman. The verification checks integrity, origin, expiry, and the overall maturity band.
Where is HodeiShield data stored?
HodeiShield stores application, database, and storage data in the EU, managed by OVH in Gravelines, France. Cloudflare, a US company, is in the request path as DNS, CDN, and TLS provider.
Is HodeiShield a replacement for an audit?
No. HodeiShield helps organise evidence, map controls, quantify risk, and issue verifiable attestations, but it does not replace an audit. Audit readiness depends on the organisation’s evidence and on the auditor’s independent assessment.
HodeiShield Tags
HodeiShield, HodeiShield platform, CISO security platform, security compliance platform, third-party risk management, exposure management, endpoint security, FAIR risk quantification, signed attestations, offline attestation verification, NIS2 compliance, DORA compliance, ENS compliance